Gadgets & Gear
6 min read•Oct 11, 2026•23
Ugreen 100W 4-Port GaN Charger Drops 27% on Amazon
Save $15 on the Ugreen 100W 4-port GaN charger, now down to $39.98. Here is how its dynamic power allocation and thermal management stack up.
PoeLLM malware has infected over 3,400 exposed Ollama and LiteLLM servers, using verse on GitHub as a stealthy command-and-control resolver for cryptominers.
Senior Technology Analyst
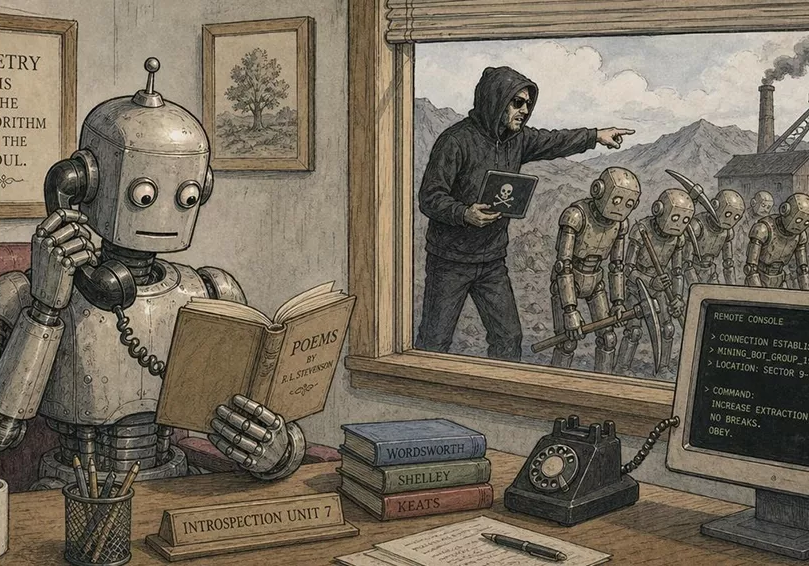
PoeLLM malware has infected over 3,400 exposed Ollama and LiteLLM servers, using verse on GitHub as a stealthy command-and-control resolver for cryptominers.
A newly uncovered threat campaign is turning the chaotic rush toward self-hosted generative artificial intelligence into a lucrative playground for illicit cryptomining. Security researchers at Lumen Technologies' Black Lotus Labs have revealed that the PoeLLM malware has compromised more than 3,400 internet-facing servers worldwide. Rather than relying on traditional domain generation algorithms or hardcoded internet protocol addresses to coordinate operations, the operators behind the campaign devised an unusually literary dead-drop mechanism: encoding live command-and-control instructions into stanzas of poetry hosted on GitHub.
The targets of this campaign are not random web servers. The attackers have zeroed in on the soft underbelly of the modern machine learning ecosystem, specifically unauthenticated deployments of Ollama and the LiteLLM proxy gateway. As engineering teams and hobbyists race to stand up local inference engines, default configurations and exposed administrative ports are leaving enterprise-grade hardware completely unprotected. Once inside, the intrusion script deploys cryptominers that siphon away the compute capacity originally provisioned to run high-throughput language models.
The most inventive component of the campaign lies in how the botnet handles communications resilience. To avoid detection by automated firewall blocklists and threat intelligence feeds, the malware uses a dead-drop resolver built directly on top of GitHub’s public code repositories. Rather than querying an obscure, high-entropy dynamic DNS domain—a signal that immediately triggers alarms in enterprise Security Operations Centers—the infection script reaches out to a public GitHub project hosting what appears to be a mundane poem.
Deep inside the lines of text, the operators established an encoding convention. By isolating four specific words embedded within the poetic phrasing and mapping their designated alphanumeric values, the client-side binary translates the text into an IPv4 address string (such as xxx.xxx.xxx.xxx). Over the course of the campaign, researchers observed the repository maintainer updating these four specific words at least 11 times.
Every time an upstream internet service provider or hosting firm terminated one of the attackers' active control servers, the repository author merely committed a four-word change to the verse. The compromised nodes periodically polled the raw GitHub repository over encrypted HTTPS, digested the modified poem, translated the four keywords into the new network coordinate, and resumed communication without skipping a beat. Because legitimate developer environments query GitHub millions of times an hour, outbound traffic to raw.githubusercontent.com rarely arouses suspicion, allowing the botnet to blend seamlessly into ordinary background noise.
While the dead-drop resolver highlights clever operational security, the root cause behind the compromise of thousands of hosts comes down to reckless network architecture. The explosive growth of local open-weight model tooling has far outpaced basic infrastructure hygiene. Tools such as Ollama have become the de facto standard for pulling and serving open models locally, listening by default on TCP port 11434. LiteLLM, widely adopted to unify disparate model interfaces under a single, OpenAI-compatible REST schema, operates similarly across port 4000.
When administrators deploy these containers inside cloud platforms like AWS, Google Cloud, or bare-metal host providers, they frequently bind services to 0.0.0.0 to simplify remote debugging or integrations with external web dashboards. Without explicit network access control lists, firewalls, or configured authentication tokens, these administrative interfaces remain completely open to any scanner crawling the global IPv4 address space.
The operators behind the PoeLLM campaign conducted aggressive port scans to locate these exposed endpoints. Upon discovery, they leveraged native execution features or remote template capabilities built into the platforms to execute arbitrary shell scripts. Because Ollama allows users to download and configure model layers through standard REST requests, malicious actors can send targeted payloads that trigger local code execution under the privileges of whichever user is running the server daemon—often root inside an improperly isolated Docker container.
Once the primary dropper achieves a foothold on an exposed server, it acts quickly to lock down the operating environment and suppress competition from other threat actors. The intrusion workflow scans the host for competing cryptominers, terminates rival processes, wipes lingering scheduled tasks, and establishes its own persistence through modified crontab schedules and custom systemd service units.
The ultimate payload delivered to these compromised machines is a heavily tuned build of the open-source XMRig Monero miner. In conventional server breaches, cryptomining incurs financial costs via inflated cloud billing or degraded web page responsiveness. In the context of large language model clusters, however, the performance degradation is far more acute.
AI inference nodes depend on massive, uninterrupted parallel compute. Systems built to run models like Llama 3 or Mistral typically pack arrays of high-end consumer GPUs, such as NVIDIA GeForce RTX 4090s, or enterprise accelerators like the A100 and H100, backed by high-core-count AMD EPYC or Intel Xeon processors. When PoeLLM’s cryptomining payloads flood host threads and saturate memory buses, inference latency spikes instantly. Tokens-per-second output collapses, GPU memory becomes fragmented, and overall power consumption hits sustained thermal limits, driving up datacenter energy expenditures while completely degrading user-facing applications.
Remediating a PoeLLM compromise involves more than terminating rogue XMRig processes. Because the payload establishes persistence across system utilities and maintains redundant connections through its GitHub dead-drop mechanism, operators must conduct a methodical cleanup.
Security teams managing self-hosted AI services should immediately verify whether their middleware interfaces are exposed to the public internet:
0.0.0.0 unless protected by a robust reverse proxy. Ensure OLLAMA_HOST is explicitly set to 127.0.0.1 or configured within an isolated software-defined network./etc/cron.*, user crontabs, and /etc/systemd/system/ for unverified unit files executing remote curl or wget commands against external repositories.The scale of the PoeLLM campaign underscores a major blind spot in modern infrastructure management. While enterprise security teams spend extensive time auditing model weights and guarding against software prompt injections, basic network perimeters around inference tooling are frequently neglected. Until developers treat AI gateways with the same strict security standards applied to relational databases, attackers will continue using inventive methods—poetic or otherwise—to exploit their compute power.
This report was independently synthesized, fact-checked, and expanded with technical mitigation guidance and risk evaluations by the Zero Hour Tech editorial desk. Initial reporting, vendor bulletins, or threat telemetry were tracked from tomshardware.com .
Contributing editor at Zero Hour Tech, specializing in gadgets & gear analysis, vulnerability response, and emerging software paradigms.
View Full Profile & Articles →Save $15 on the Ugreen 100W 4-port GaN charger, now down to $39.98. Here is how its dynamic power allocation and thermal management stack up.
SoftBank pursues a $100 billion AI fund backed by Middle Eastern wealth, aiming to buy low-tech enterprises and rebuild them with robotics and automation.
Get our concise weekly security briefings covering newly disclosed vulnerabilities, exploit mechanics, and actionable system hardening guides.
100% Privacy guaranteed. One-click unsubscribe at any time.